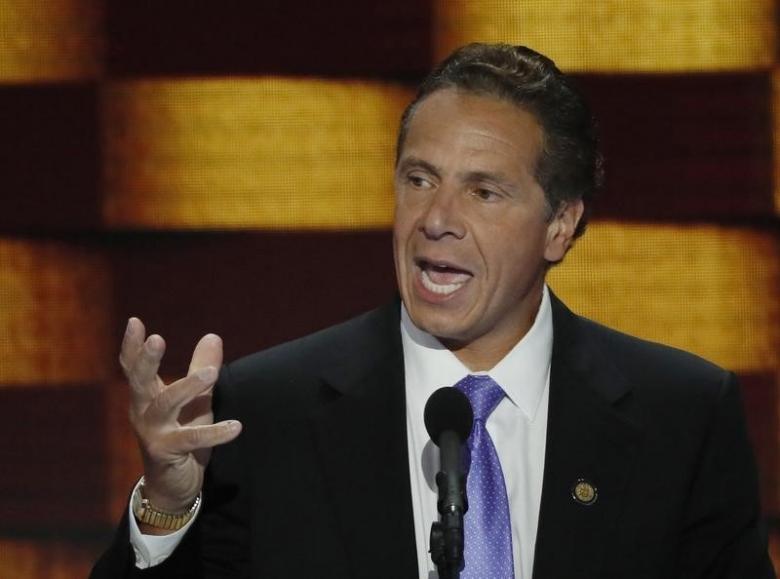
New York state Governor Andrew Cuomo speaks on the final night of the Democratic National Convention in Philadelphia, Pennsylvania, U.S. July 28, 2016. REUTERS/Mike Segar
New York Governor Andrew Cuomo on Tuesday issued long-anticipated proposed cyber regulations for banks and insurers in the state, the first of their kind in the United States by any state or federal agency, the governor said in a statement.
Cuomo’s planned regulations for institutions overseen by the New York State Department of Financial Services (NYDFS) would require companies to set up cyber security programs and appoint a chief information officer, among other measures, according to the governor’s office.
The planned regulations, in the works since 2014, follow a series of high-profile hackings of U.S. companies and three surveys by the regulator about cyber security programs at a total of nearly 200 companies under its watch. One NYDFS report last year revealed that a third of 40 banks in a 2014 survey did not require outside vendors to notify them of data breaches, which could compromise bank data.
The regulations aim to provide institutions with flexibility to adapt to technological innovations while reducing vulnerabilities, NYDFS Superintendent Maria Vullo said in a statement.
NYDFS regulates state-chartered and foreign banks licensed to operate in the state, including Goldman Sachs Group, Barclays and Deutsche Bank, and all insurance companies that do business in the state.
It previewed the plan in a November, 2015 letter to other state and federal regulators. That same day, U.S. prosecutors unveiled criminal charges accusing three men of helping run a sprawling series of hacking and fraud schemes, including a huge 2014 attack against JPMorgan Chase & Co , that generated hundreds of millions of dollars of illegal profit.
Among the planned requirements: board chairmen would have to file annual certifications with NYDFS, stating, to the best of their knowledge, that their companies’ cyber programs comply with the regulation.
Other measures would include appointing overseers for outside vendors and limiting access of customers’ non-public information, such as social security numbers, to employees who need those details, according to the proposal. Systems would have to include multiple steps for verifying user identities.
Institutions would also have to regularly test their cyber security systems. The chief information security officer would have to present twice-yearly reports about progress and vulnerabilities to the board of directors and make those findings available to NYDFS.
Before the plan becomes final, the public will have 45 days to submit comments, once the proposed regulations are published in the New York State Register.
Source: Reuters.com
The Forex market does not always offer clear trading opportunities. Sometimes, price moves sharply in…
Open social media for a few minutes and you can easily find someone talking about…
EURUSD, GBPUSD, USDJPY, Gold and Bitcoin remain at important technical levels as volatility and geopolitical…
A winning trade feels good. A series of winning trades feels even better. Confidence increases.…
The Forex and commodities markets are entering an interesting phase, with renewed inflation concerns, expectations…
Central banks do more than change interest rates. They also influence financial markets through the…
View Comments
Thanks to the team of Reuters! Very interesting subject indeed.
Its very kind of you to share such useful information, thanks Vlad.
Just read, interesting Vlad
Very informative..
Many people should come forward to share their comments...
Got to know more about cyber regulations for banks and insurers